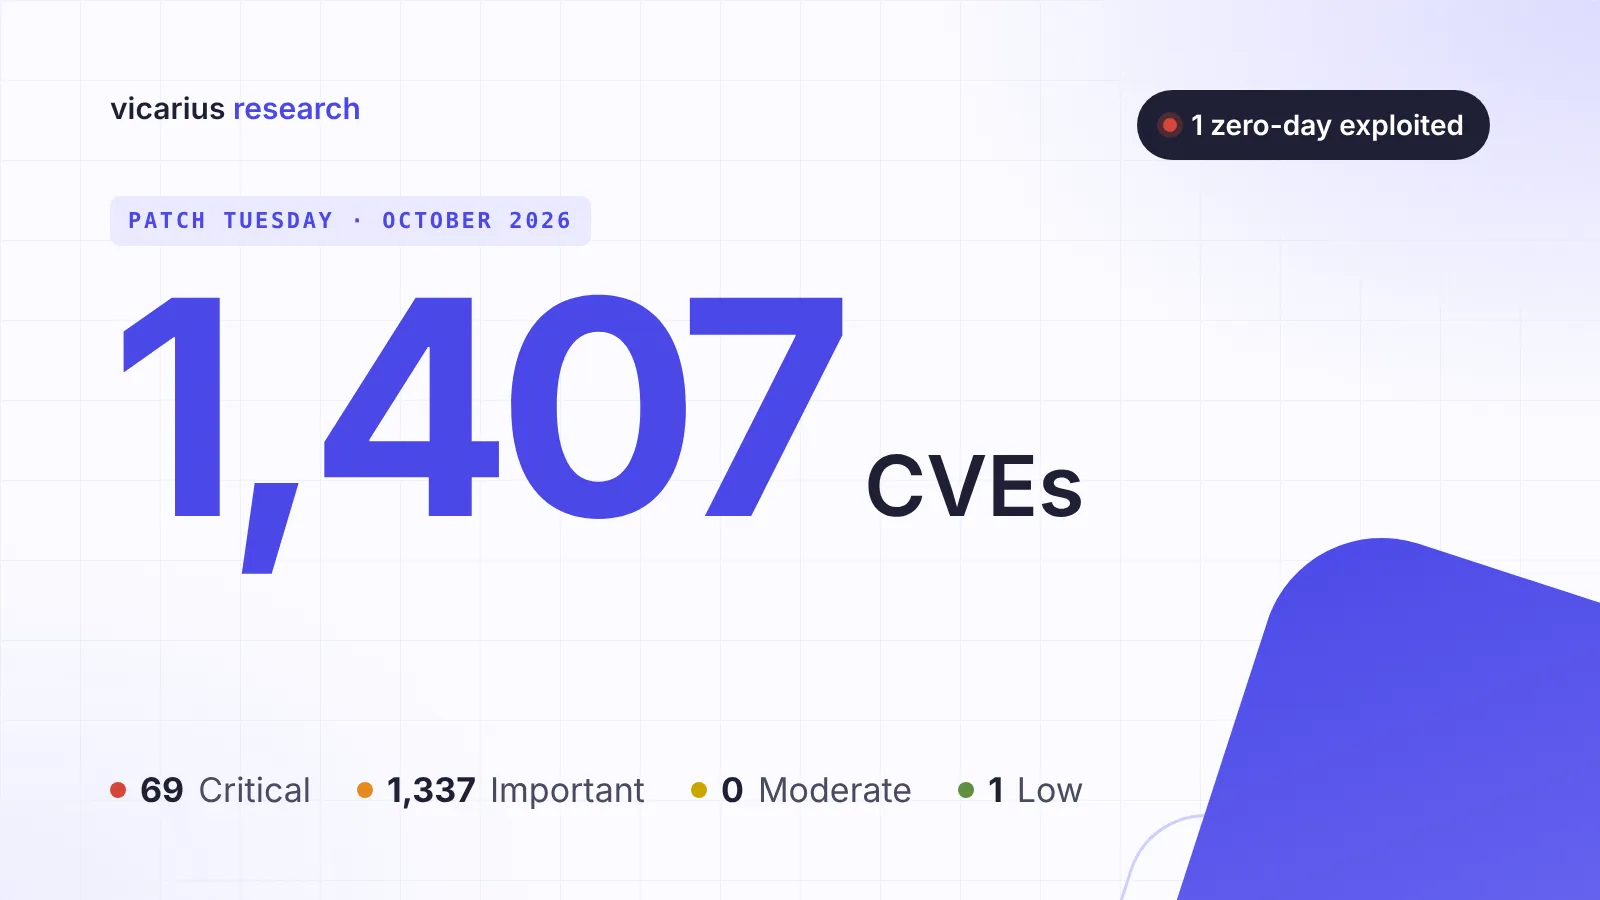


Microsoft patched 1,407 CVEs in its October 2026 Patch Tuesday, the largest release on record and 46% more than September's previous record of 964. One of them, a Mark of the Web bypass in Windows Shell, was exploited in the wild as a zero-day.
Key takeaways
• 1,407 CVEs: 69 critical, 1,337 important and one low. Volume rose 46% from September, while critical CVEs fell from 104 to 69.
• One exploited zero-day: CVE-2026-96951 (Windows Shell) lets attackers evade Mark of the Web defenses. CISA has added it to the KEV catalog. A .NET Framework flaw that bypasses Windows Defender Application Control, CVE-2026-108398, was publicly disclosed before the release.
• Exchange, Active Directory and Outlook carry the highest risk. Microsoft rates the critical Exchange Server RCE CVE-2026-70571 and the Active Directory Domain Services RCE CVE-2026-70229 "Exploitation More Likely", as well as the Exchange mailbox-access flaw CVE-2026-96940. Five critical Outlook RCEs can be triggered from the Reading Pane.
• Infrastructure services are exposed to unauthenticated attackers: DHCP Server (CVE-2026-96934), DNS Server (CVE-2026-83869), Microsoft QUIC (CVE-2026-100219) and Message Queuing (CVE-2026-100202) all have RCEs with a CVSSv3 score of 9.8.
Of the 1,407 CVEs patched this month, 69 are rated critical, 1,337 are rated important and one is rated low. Microsoft rates 109 of them "Exploitation More Likely", and 54 carry a CVSSv3 score of 9.8 or higher.
A record-breaking release
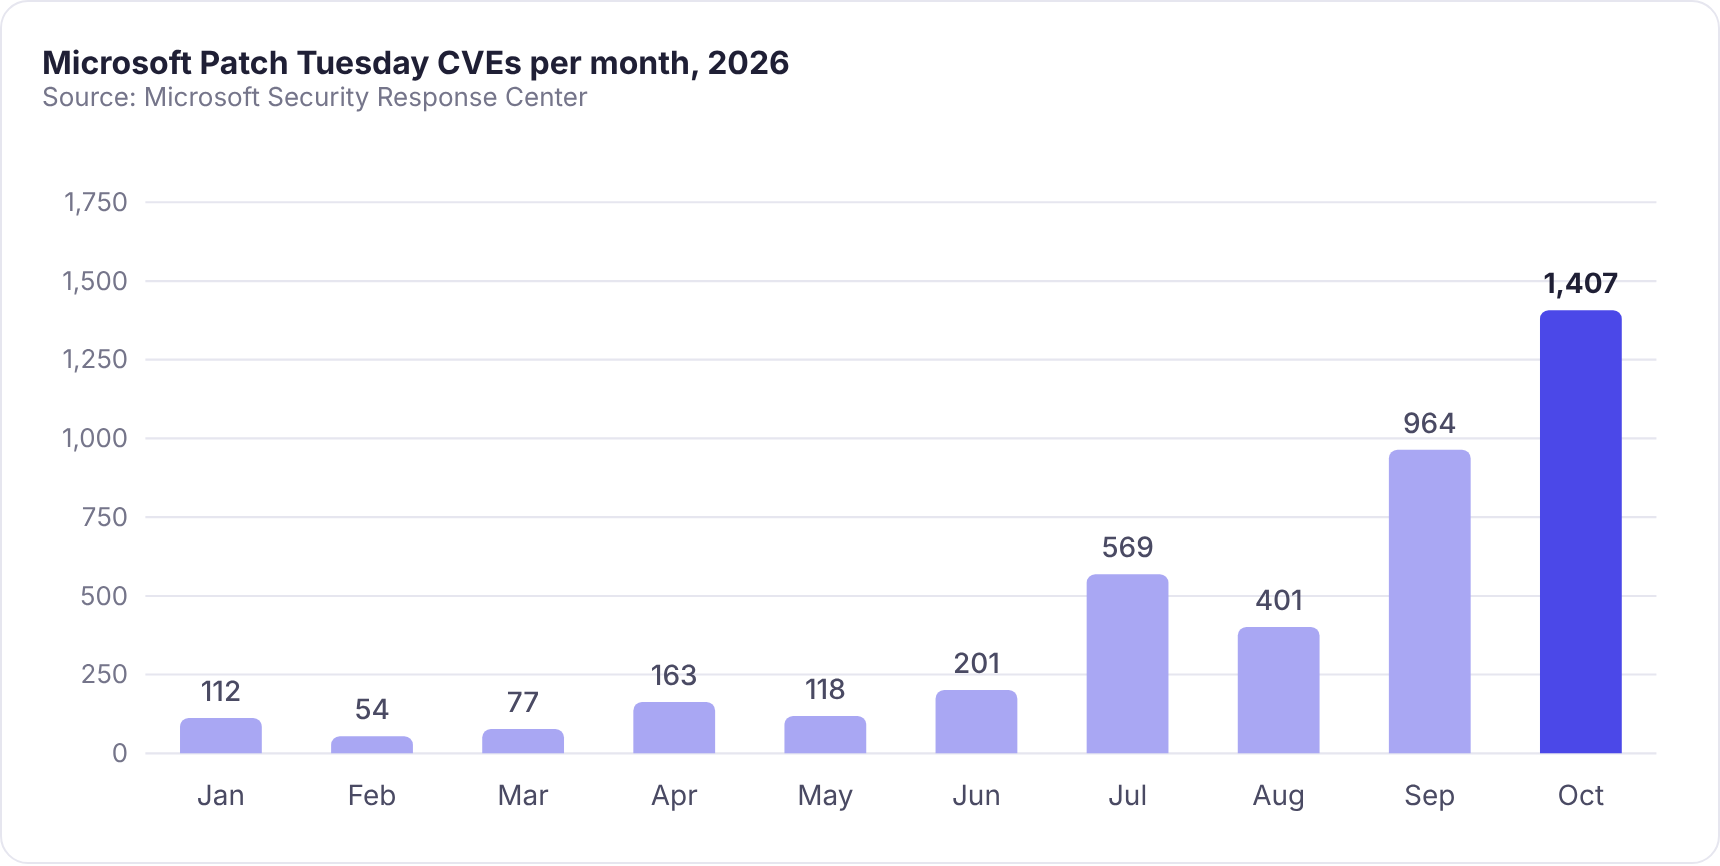
October's 1,407 CVEs are the most Microsoft has fixed in a single Patch Tuesday. The release surpasses September's 964, which was itself a record, as well as July's 569 and August's 401. Before summer 2026, no Patch Tuesday had exceeded about 200 CVEs. Through October, Microsoft has patched 4,066 CVEs in 2026's Patch Tuesday releases.
What was patched
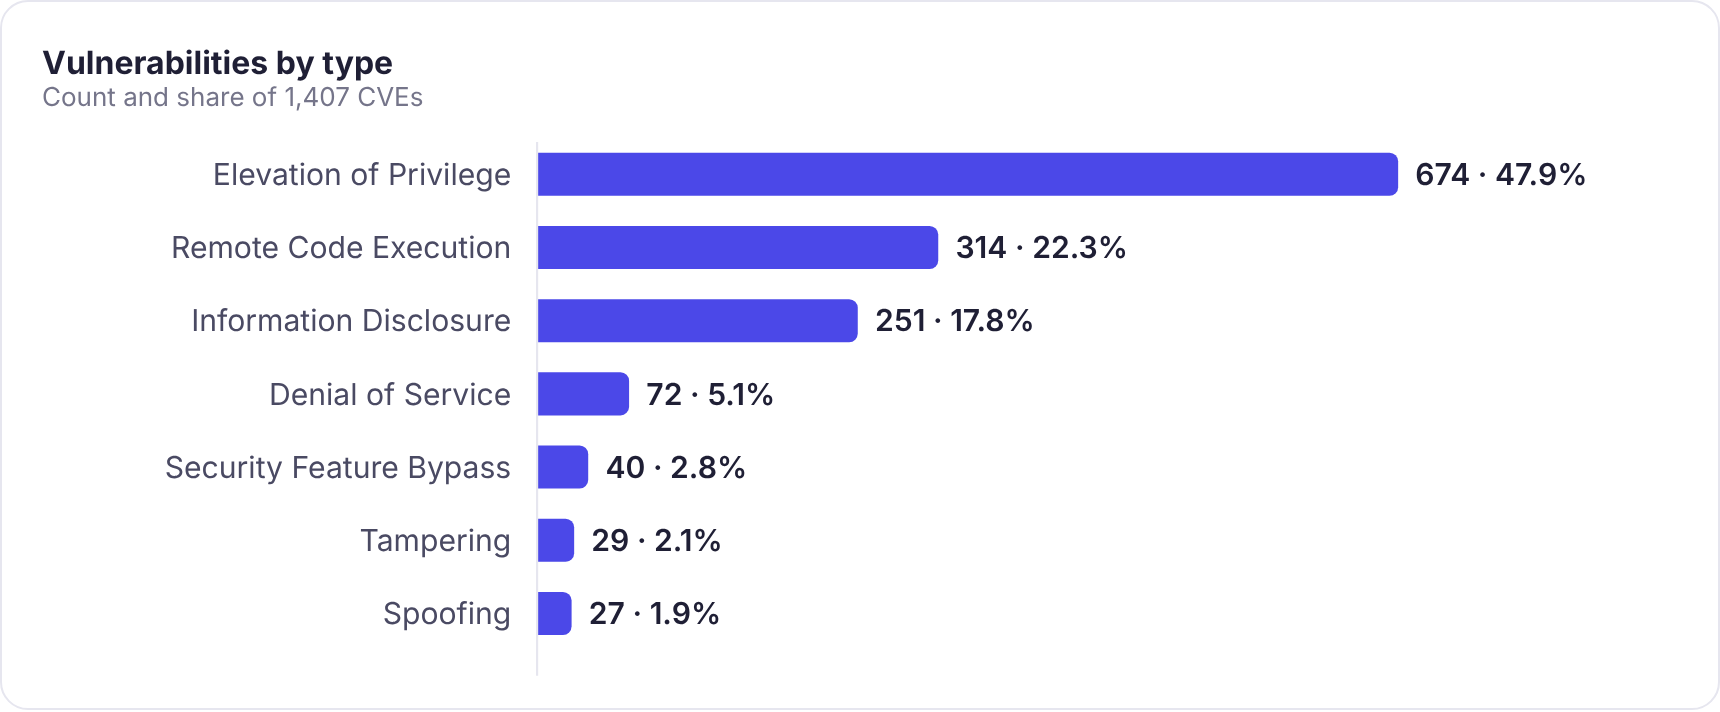
Elevation of privilege vulnerabilities accounted for 47.9% of the CVEs patched this month (674), followed by remote code execution at 22.3% (314) and information disclosure at 17.8% (251). Remote code execution dominates the critical tier: 56 of the 69 critical CVEs are RCEs.
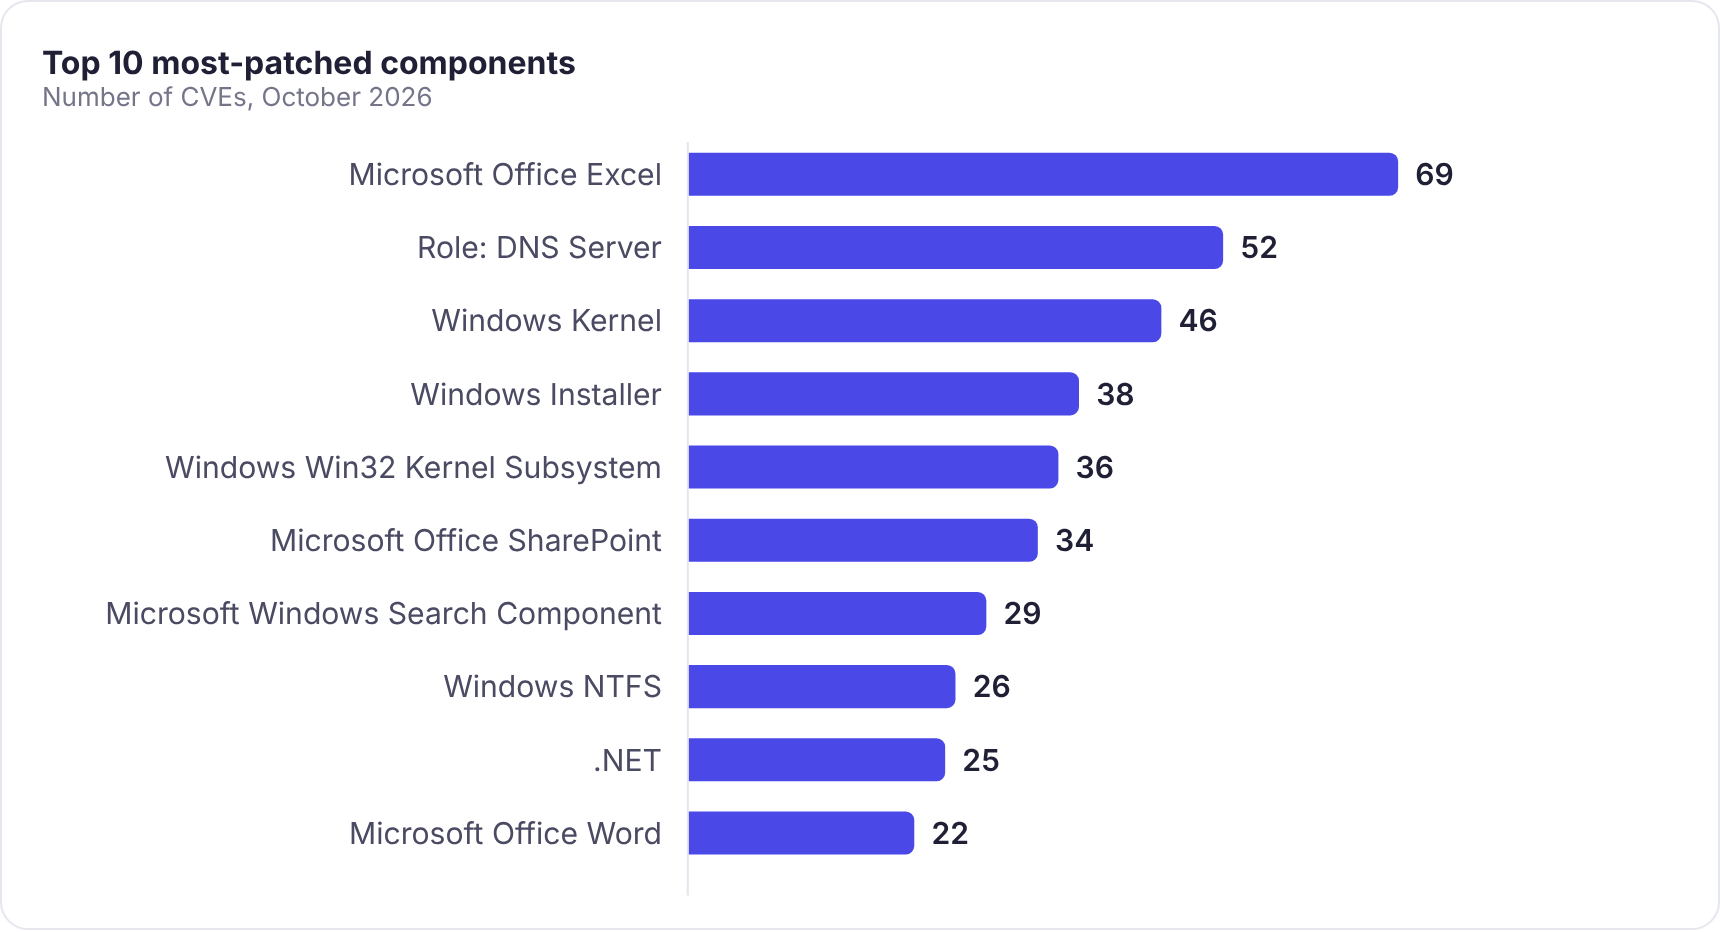
This month's update includes patches for 301 product families and components:
Zero-day exploited in the wild
Important
CVE-2026-96951 | Windows Shell security feature bypass vulnerability
CVE-2026-96951 is a command injection flaw (CWE-77) in Windows Shell with a CVSSv3 score of 8.8. According to Microsoft, an attacker who exploits it could evade Mark of the Web (MOTW) defenses, the tag Windows applies to files from the internet so that they are treated as untrusted. Exploitation requires the victim to act: the attacker would need to convince a user to open a specially crafted file, for example one sent as an email or instant message attachment, or reached through a link to an attacker-controlled site. According to Microsoft, it was exploited in the wild as a zero-day.
Since January 2022, Microsoft has patched 32 vulnerabilities in Windows Shell or its Mark of the Web feature, and CVE-2026-96951 is the seventh of them to be exploited as a zero-day. The earlier ones were two Mark of the Web bypasses in November 2022 (CVE-2022-41091 and CVE-2022-41049), two more in August and September 2024 (CVE-2024-38213 and CVE-2024-38217), and two Windows Shell flaws earlier this year: CVE-2026-21510 in February and CVE-2026-32202 in April. CISA added CVE-2026-96951 to its Known Exploited Vulnerabilities (KEV) catalog on October 13, 2026, with a federal remediation due date of October 16, 2026.
Other notable vulnerabilities
Important
CVE-2026-108398 | .NET Framework security feature bypass vulnerability
CVE-2026-108398 is an untrusted search path flaw (CWE-426) in .NET Framework with a CVSSv3 score of 8.8. According to Microsoft, an authenticated attacker could place a specially crafted .NET assembly on an affected system and register it for loading by a protected process. That would bypass Windows Defender Application Control (WDAC) enforcement and let the attacker run code inside the protected process, with no user interaction. The flaw was publicly disclosed before the release. Microsoft rates it "Exploitation Less Likely", but organizations that rely on WDAC to block unauthorized code should treat it as a priority.
Critical
CVE-2026-70242 | Microsoft Office Outlook remote code execution vulnerability
CVE-2026-70242 is a heap-based buffer overflow (CWE-122) in Microsoft Office Outlook with a CVSSv3 score of 9.8. According to Microsoft, an attacker could send a specially crafted email, and simply viewing it in the Outlook Reading Pane could trigger the vulnerability without the recipient opening the message or clicking anything in it. Successful exploitation could let the attacker run code on the recipient's system. It is one of five critical Outlook RCEs this month, and Microsoft lists the Reading or Preview Pane as an attack vector for all five. Microsoft rates them "Exploitation Less Likely", but a zero-click email vector puts every unpatched Outlook desktop in scope.
Other critical Outlook RCEs patched this month (4)
Critical
CVE-2026-70571 | Microsoft Exchange Server remote code execution vulnerability
CVE-2026-70571 is a stack-based buffer overflow (CWE-121) in Exchange Server with a CVSSv3 score of 8.1. According to Microsoft, an unauthenticated attacker could send a specially crafted email to an affected Exchange server, triggering an internal content-conversion process, and run code on the server. No user interaction is required. Microsoft notes that exploitation requires a deep understanding of the target environment and is not guaranteed to succeed, yet it rates the flaw "Exploitation More Likely". Because the attack only requires delivering an email to the server, it is a priority for on-premises Exchange.
Important
CVE-2026-70279 | Microsoft Exchange Server spoofing vulnerability
CVE-2026-70279 is a cross-site scripting flaw (CWE-79) in Exchange Server with a CVSSv3 score of 9.3. According to Microsoft, an unauthenticated attacker could send a specially crafted link to a user and persuade them to click it. If a user with administrative privileges clicks the link, the attacker could perform actions with that user's privileges, potentially accessing or modifying organizational data. Microsoft rates it "Exploitation More Likely".
Important
CVE-2026-96940 | Microsoft Exchange Server elevation of privilege vulnerability
CVE-2026-96940 is a weak authentication flaw (CWE-1390) in Exchange Server with a CVSSv3 score of 8.8. Microsoft first published it on October 2, ahead of Patch Tuesday. According to Microsoft, an authenticated attacker who exploits it could gain unauthorized access to other users' mailboxes within the same organization and read their email messages and attachments. It does not allow access across tenant boundaries. Microsoft has already deployed a fix for Exchange Online, so only on-premises Exchange Server customers need to install the update. Microsoft rates it "Exploitation More Likely".
Critical
CVE-2026-70229 | Windows Active Directory Domain Services remote code execution vulnerability
CVE-2026-70229 is an incorrect authorization flaw (CWE-863) in Active Directory Domain Services with a CVSSv3 score of 8.1. According to Microsoft, an unauthenticated attacker could send a specially crafted packet to an affected service over the network and run code on the target system, with no user interaction. Microsoft says exploitation depends on specific network configurations and timing conditions, which is why the attack complexity is high, but it still rates the flaw "Exploitation More Likely". Code execution on a domain controller would put the whole domain at risk, which makes this one of the month's most important fixes.
Critical
CVE-2026-96934 | Windows DHCP Server remote code execution vulnerability
CVE-2026-96934 is a use-after-free flaw (CWE-416) in Windows DHCP Server with a CVSSv3 score of 9.8, meaning it is network-exploitable with no authentication or user interaction. According to Microsoft, an unauthenticated attacker could send a specially crafted packet to an affected service and run code on the target system. Microsoft patched 16 DHCP Server CVEs this month, including five more RCEs that are rated critical or score 9.8.
Other DHCP Server RCEs rated critical or scoring 9.8 (5)
Important
CVE-2026-83869 | Windows DNS Server remote code execution vulnerability
CVE-2026-83869 is an integer underflow (CWE-191) in Windows DNS Server with a CVSSv3 score of 9.8. According to Microsoft, an unauthenticated attacker could send a specially crafted packet to an affected service over the network and run code on the target system, with no user interaction. DNS Server was the second most-patched component this month, with 52 CVEs, and Microsoft rates every DNS Server RCE important rather than critical. Given the role DNS servers play, and that they often run on domain controllers, we recommend treating the highest-scoring ones as critical.
Other DNS Server RCEs with a CVSSv3 score of 8.8 or higher (8)
Critical
CVE-2026-100219 | Microsoft QUIC remote code execution vulnerability
CVE-2026-100219 is a use-after-free flaw (CWE-416) in Microsoft QUIC with a CVSSv3 score of 9.8. According to Microsoft, an unauthenticated attacker could send a specially crafted packet to an affected service over the network and run code on the target system, with no authentication or user interaction. A second critical QUIC RCE, CVE-2026-105016, also scores 9.8. Microsoft rates both "Exploitation Less Likely". The same profile applies to CVE-2026-100202, a critical 9.8 use-after-free in the Windows Message Queuing (MSMQ) Queue Manager that can be triggered by a specially crafted message sent to a system running the MSMQ service.
Patch-first list
The list below is ordered by real-world risk: exploitation first, then flaws reachable by unauthenticated attackers or with no user interaction, then Microsoft's exploitability rating. The complete list of all 1,407 CVEs, with severity, CVSS, exploitability and root cause, is in the companion spreadsheet.
How Vicarius helps
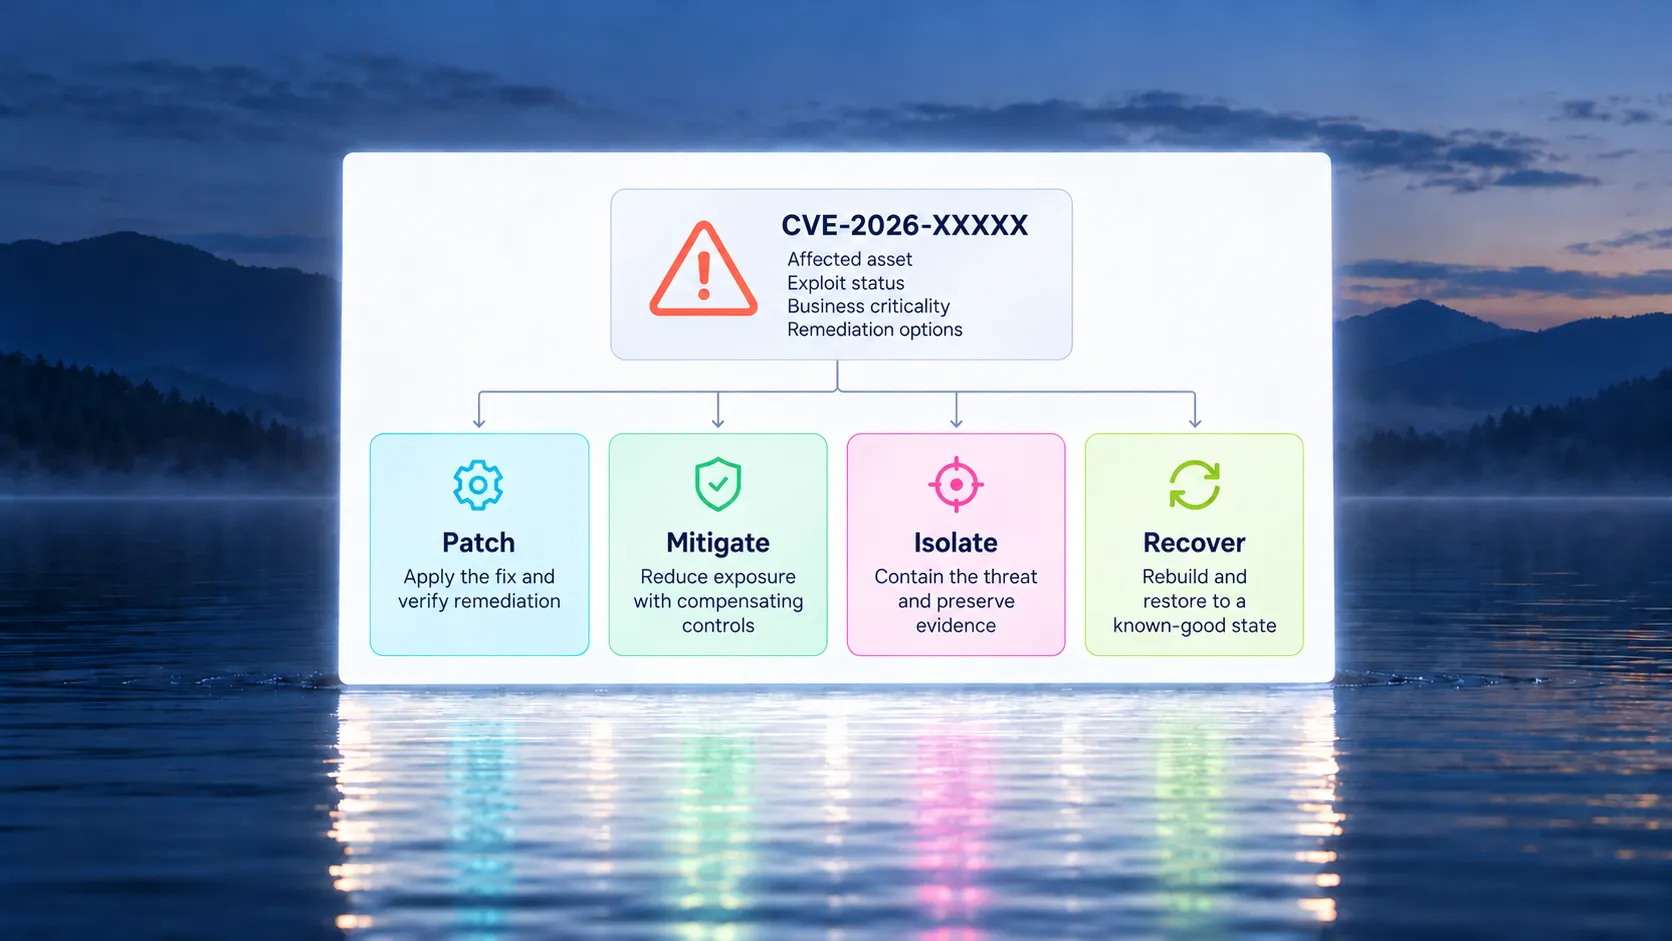
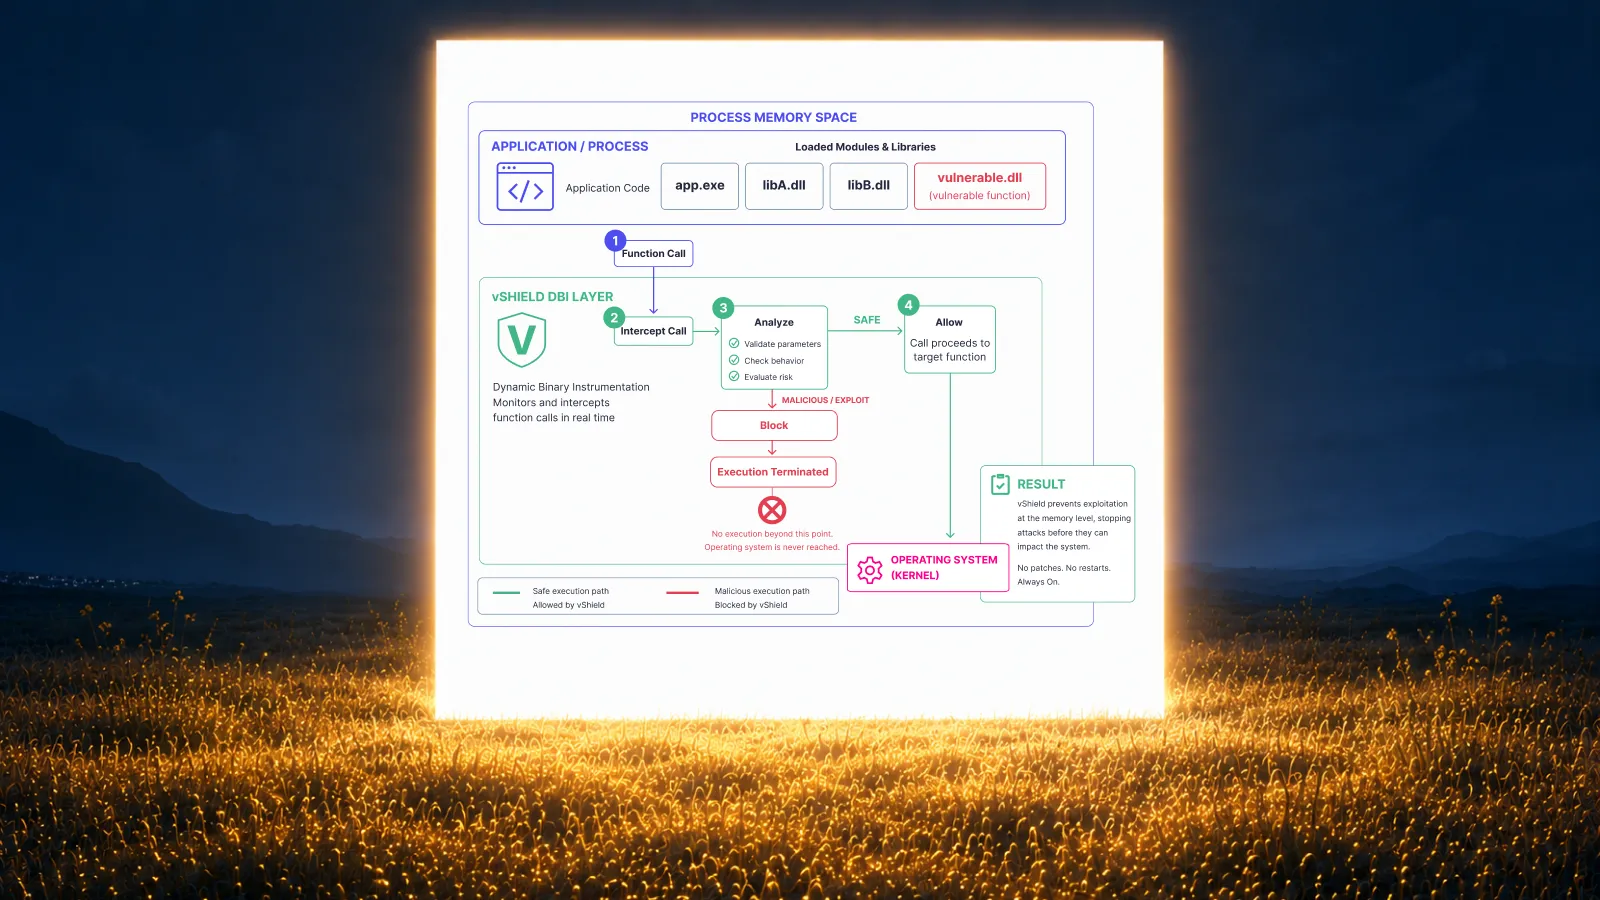
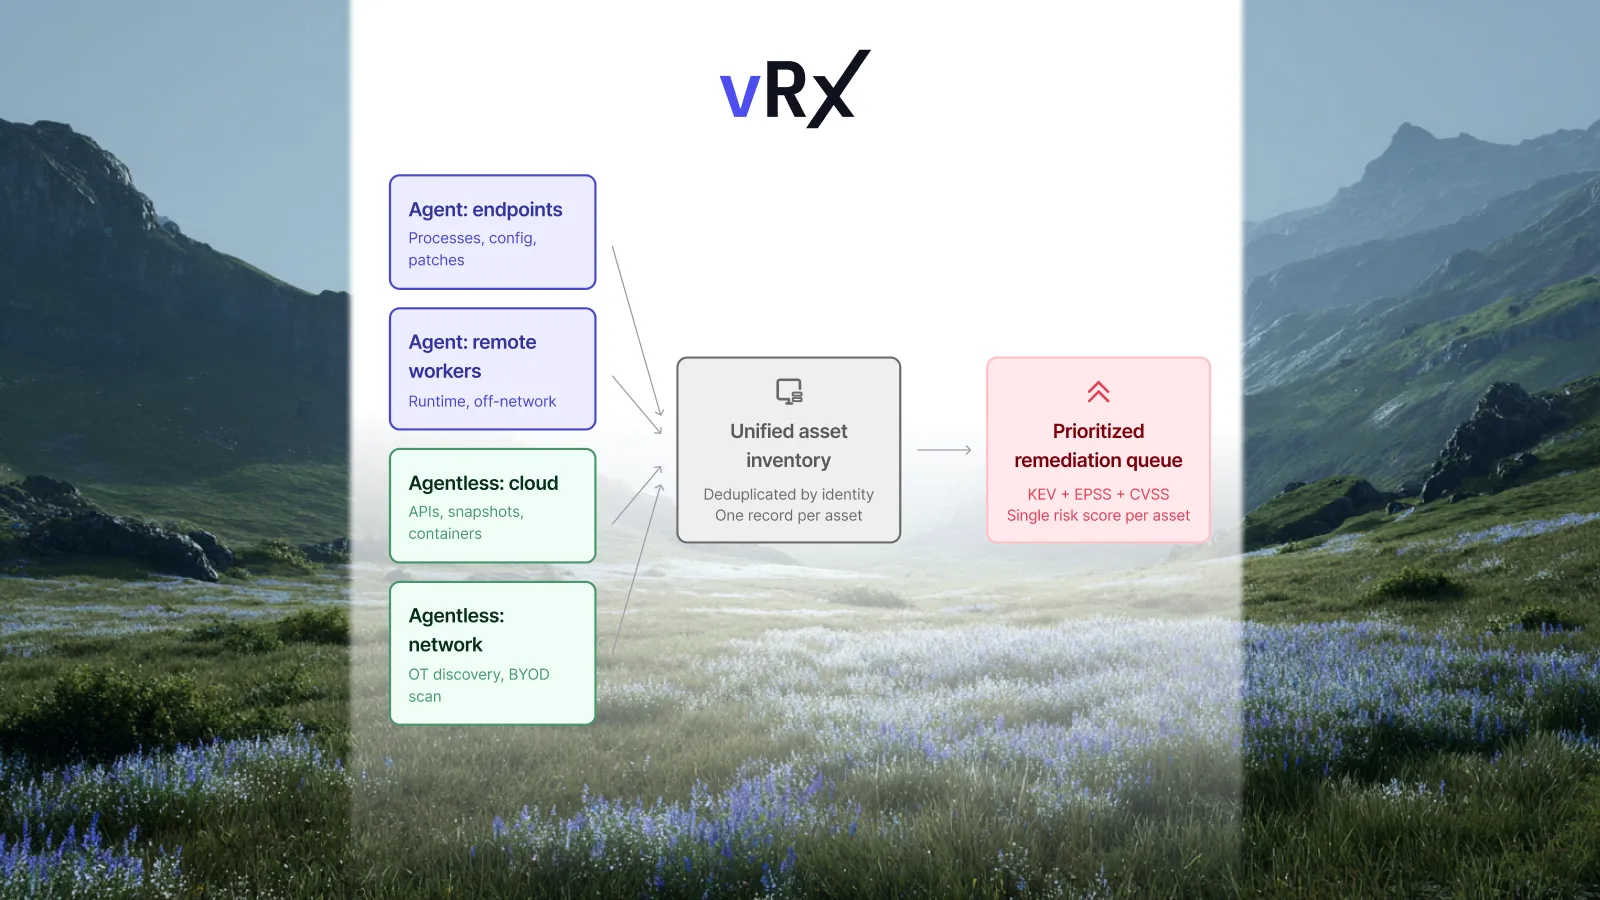
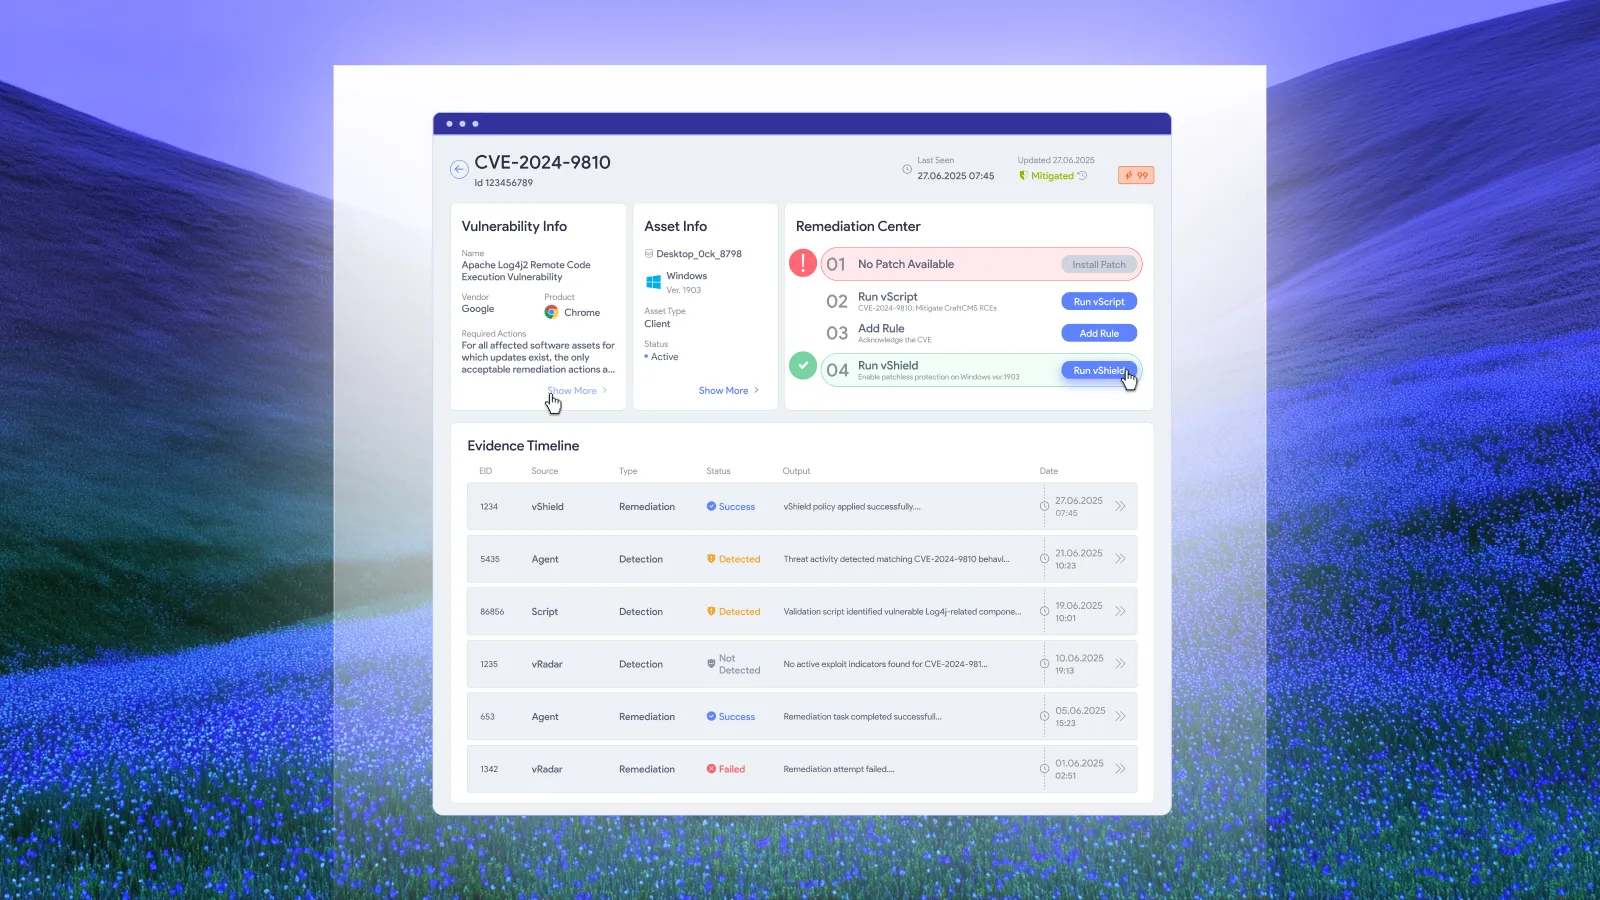
A release of 1,407 CVEs cannot be patched in one pass. vRx identifies which of this month's vulnerabilities are present on your Windows and Office assets and prioritizes them by exploitation and exposure, so the zero-day, the Exchange and Active Directory flaws and the network-facing RCEs come first.
vRx patch management deploys Microsoft's October updates alongside third-party patches from the Apps & OS patch catalog. Where a patch cannot be applied right away, for example on a domain controller or Exchange server waiting for a maintenance window, patchless protection helps reduce exposure until the update is installed.
Frequently asked questions
How many vulnerabilities did Microsoft fix in October 2026 Patch Tuesday?
Microsoft fixed 1,407 CVEs in October 2026 Patch Tuesday: 69 critical, 1,337 important and one low. It is the largest Patch Tuesday on record, ahead of September 2026's 964.
Were any October 2026 Patch Tuesday vulnerabilities exploited in the wild?
Yes. Microsoft says CVE-2026-96951, a security feature bypass in Windows Shell that evades Mark of the Web defenses, was exploited in the wild as a zero-day, and CISA has added it to the KEV catalog. One other CVE, CVE-2026-108398 in .NET Framework, was publicly disclosed before the release.
What should I patch first?
Start with the exploited zero-day CVE-2026-96951, then on-premises Exchange Server (CVE-2026-70571, CVE-2026-70279, CVE-2026-96940), domain controllers (CVE-2026-70229), Outlook (CVE-2026-70242 and four related critical RCEs), and network services such as DHCP Server, DNS Server, QUIC and Message Queuing. The patch-first list above gives the full order.
Related reading
• Patch verification checklist: how to prove a vulnerability is fixed
• Vulnerability remediation SLAs: how to set deadlines that reduce exposure
• Only 1.48% of CVEs were confirmed exploited. What should vulnerability teams do?
Sources
• Microsoft October 2026 Security Updates release notes